

@glinr/theauth-expo brings theAuth auth to React Native and Expo apps. It stores session tokens in any storage adapter you choose. AsyncStorage, SecureStore, or your own, and sends them via Authorization header rather than cookies.
Installation
Setup
1
Secure token storage
For production apps, useexpo-secure-store to keep the session token in the Keychain (iOS) or Keystore (Android):
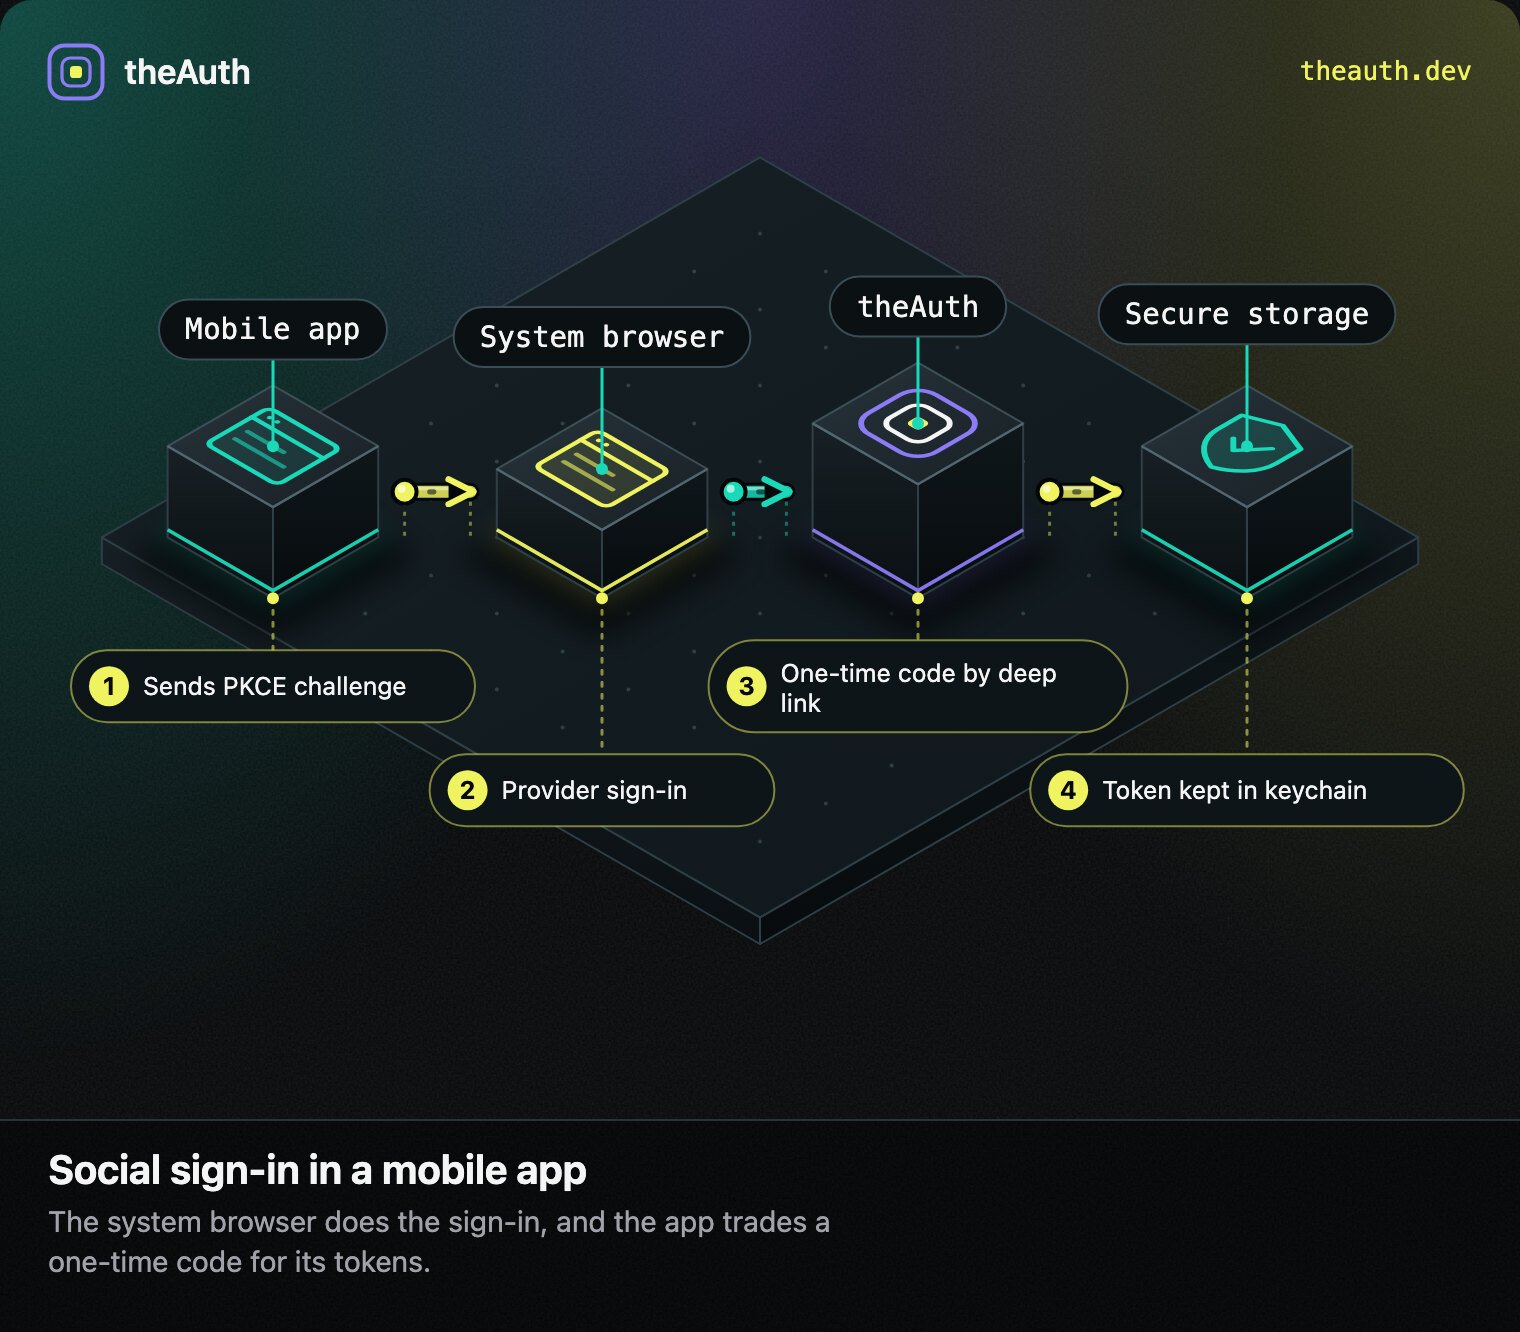
Mobile sign-in with the system browser and a one-time code.
Social sign-in
The app opens the provider in the system browser, and the server sends the browser back to your app with a single-use code. The app trades that code, together with a PKCE verifier that never left the device, for a session. The session token is never placed in a URL.1
Allow your app's redirect URI on the server
mobile, the mobile flow is off.2
Configure the provider in the app
3
Call the hook
signInWithProvider returns a failure whose message names the gate (two_factor_required). Complete the factor, then sign in again.
The mount path in basePath must expose the OAuth plugin routes /auth/oauth/authorize/:provider and /auth/oauth/mobile/exchange. The OAuth provider’s own redirect URI stays your server callback, not the app link.
Refresh on foreground
Pass React Native’sAppState as appState and the session is re-checked every time the app comes back to the foreground, so a session revoked elsewhere signs the user out.
Passkeys
Pass a platform authenticator and the provider can sign users in with a passkey and add one to a signed-in account. The server’s passkey routes already return WebAuthn JSON options and a session token, soreact-native-passkey works as is:
registerPasskey needs a session, so call it after another sign-in method. Your app’s associated domains (iOS) and Digital Asset Links (Android) must list the relying party ID the server uses. A required second factor comes back as a failure naming the gate, the same as social sign-in.
Custom fetch (DPoP, pinning)
Every request the provider makes goes throughconfig.fetch when set. Pass a DPoP client’s fetch from @glinr/theauth-client to attach proofs, or your own pinned-certificate implementation:
crypto.subtle by default, so supply one (for example react-native-quick-crypto) and generate the key pair with it. Session tokens are plain bearer tokens on the server today, so proofs are useful for OAuth and MCP access tokens you also send through this fetch.
Hooks reference
useSession
useUser
useSignIn
useSignUp
Email and password
By defaultsignIn and signUp call the username routes. Set emailPassword: true in the provider config to call the core email and password routes instead (POST {basePath}/auth/email/sign-in and /auth/email/sign-up, body field email), served when the server sets the emailPassword config (see Email and password).
signUp resolves to data.verificationRequired === true and the user stays signed out. A sign-in before verification fails with code: "EMAIL_NOT_VERIFIED". The verify and reset steps are plain POST calls to /auth/email/verify and /auth/email/reset-password, usually from the web page the emailed link opens, so the Expo provider does not wrap them.
useSignOut
useAgents
AuthExpoConfig
Related
React
Hooks and components for web React apps.
Client SDK
Framework-agnostic fetch client for non-React environments.
Sessions
Session model details including JWT token refresh flows.
OAuth providers
Configure social sign-in providers for the OAuth redirect flow.