

theAuth runs the sign-in for the humans who own agents. Each method is either a plugin or a config key on
createTheAuth that you opt into, use only what your app needs. Methods that issue sessions (magic link, email OTP, username, phone, OAuth) need auth.session configured.If you already run Clerk, Auth.js, or better-auth, keep them and skip the plugins. Plug into an existing provider.Sign-in methods
Email and password
Why there is no email plus password plugin, and the options.
Username and password
Built-in password auth with PBKDF2-SHA256 hashing.
Magic link
Single-use link in an email, no password.
Email OTP
Six-digit code via email.
Phone OTP
SMS code, you supply the delivery function.
Passkey
WebAuthn / FIDO2 biometrics and security keys.
Sign-in with Ethereum
EIP-4361 wallet-based sign-in.
Device code
For TVs and CLIs that can’t take a password.
Two-factor
TOTP with backup codes.
Captcha
Turnstile, hCaptcha, reCAPTCHA token verification.
Anonymous
Throwaway sessions, upgrade on sign-up.
Google One Tap
Google’s one-tap sign-in widget.
OAuth proxy
Reverse-proxy mode for trusted ingress.
OAuth providers
Thirty-eight first-class providers, plus a generic factory for anything with a standard authorization code flow.- Popular
- Work
- Developer
- Payments
- Enterprise
GitHub
Apple
Microsoft
Discord
Slack


How plugins fit
Plugins register routes atcreateTheAuth() time, and the instance serves them through theauth.plugins.handleRequest(request) (framework adapters do this for you, mounted under /api/theauth by default). Several methods are also available as config keys that expose a module on the instance, for example username, phone, magicLink, emailOtp, totp, passkey, org, sso, admin, apiKeys and captcha. Those properties are null unless the matching config key is passed.
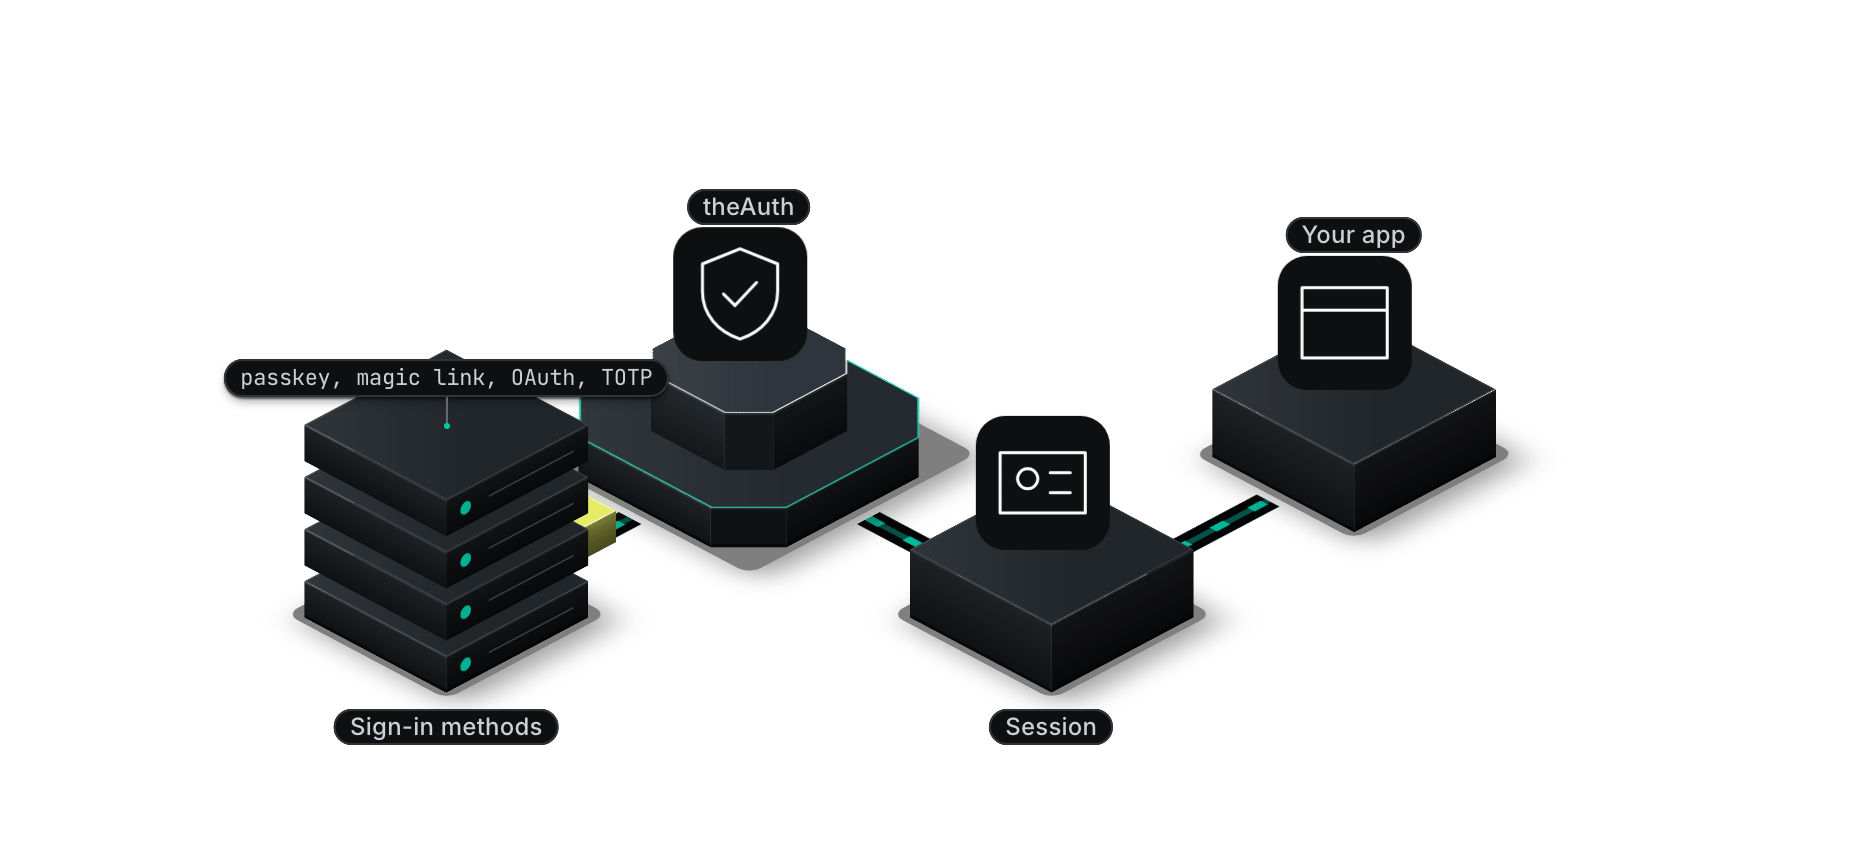
Sign-in methods feed one session through theAuth into your app.
auth.adapter (for example bearerAuth) or auth.session, then resolve the user from a request:
resolving a user from a request
theauth.auth.resolveUser uses the configured auth.adapter. It returns null when no adapter is set, even if auth.session is configured.
Once the user is resolved, theAuth is done with human auth. The rest of the stack (agents, permissions, audit) hangs off
user.id.Enterprise identity
Organizations
Multi-user accounts, roles, invitations.
SSO / SAML
SAML 2.0 and OIDC SSO.
SCIM
Automated provisioning from your IdP.
Admin plugin
Ban, impersonate with TTL, audit.
API keys
For machine-to-machine callers.
OIDC provider
Turn your theAuth instance into an IdP for other apps.
Related
Agent identity
The agent layer that sits on top of human authentication.
Sessions
How theAuth manages session lifetime and cookie settings.
Quickstart
Get a working theAuth instance running in minutes.
Adapters overview
Mount auth routes on Hono, Next.js, Express, and more.