

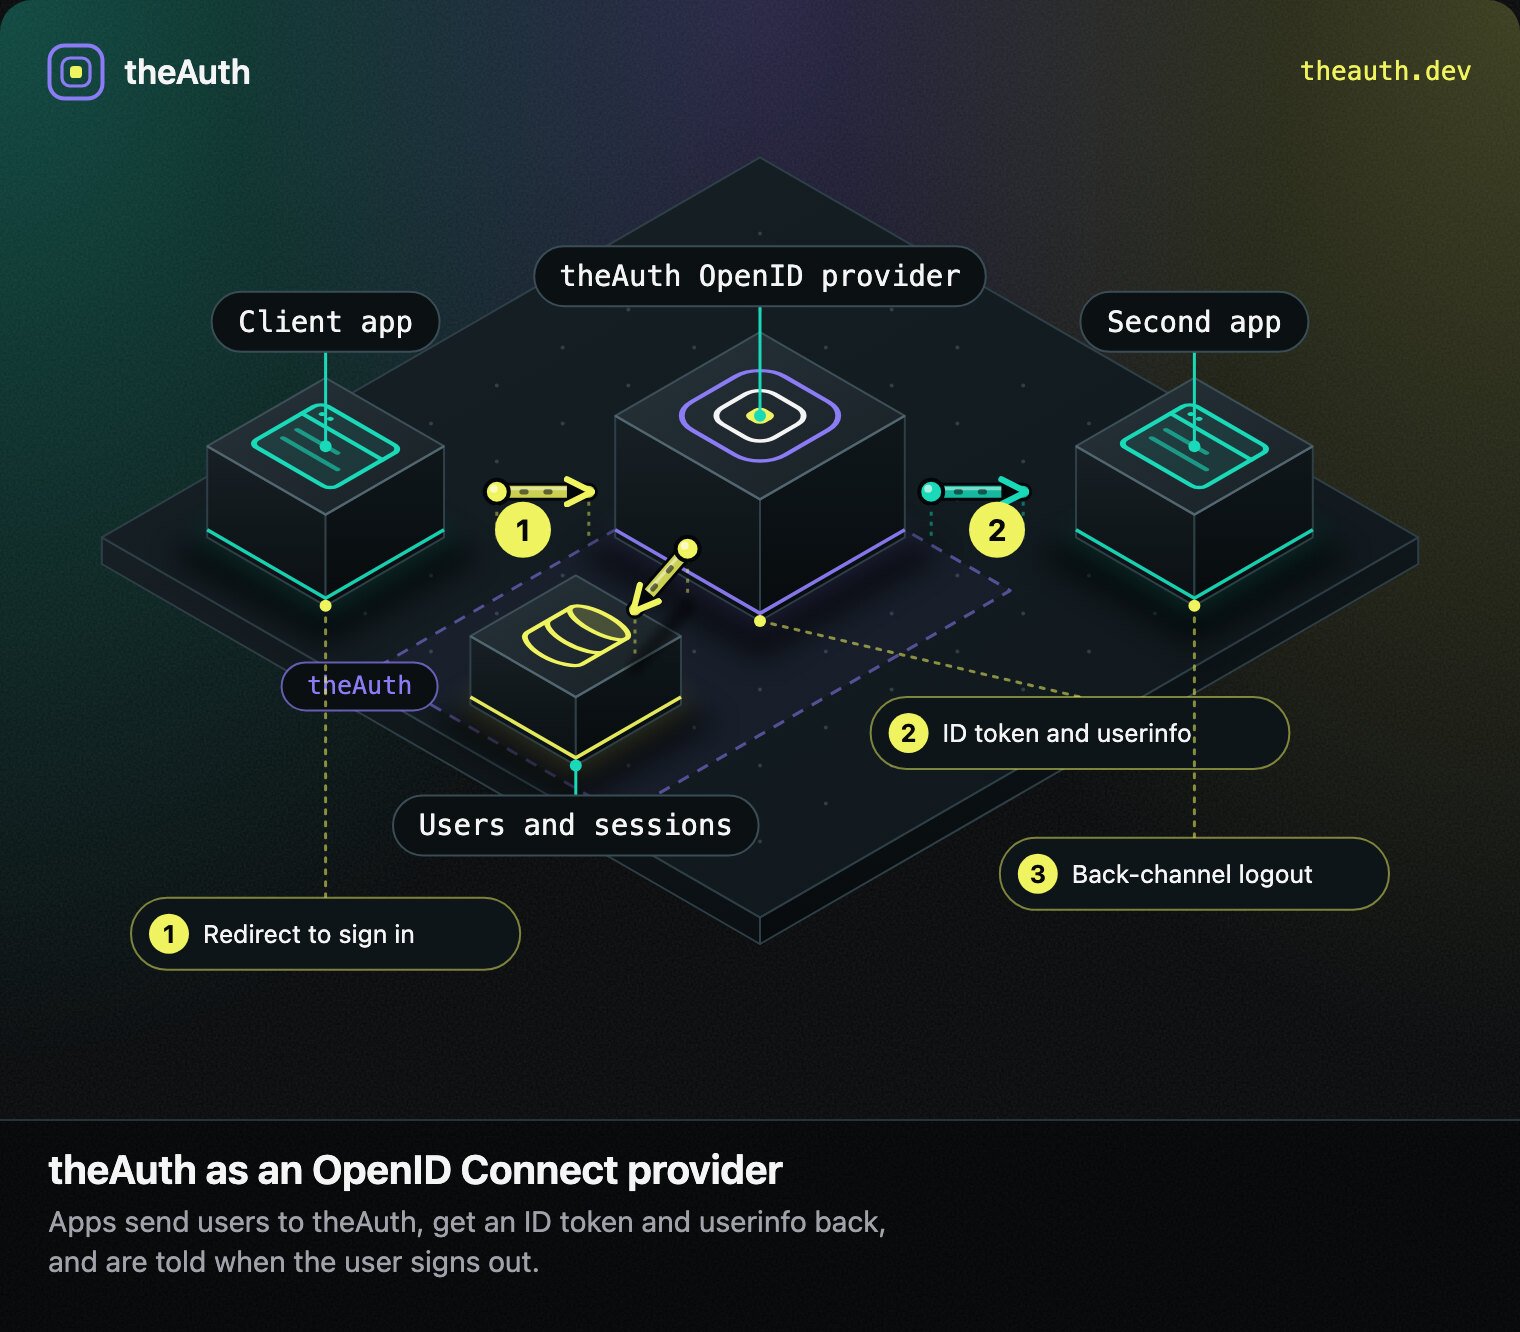
theAuth as the identity provider for your other apps.
Setup
1
2
Configuration options
Authorization code flow
createOidcProviderModule returns a module of methods. It does not register any HTTP routes, so you mount the endpoints in your own server and call the matching method from each handler.
- Client redirects the user to your authorization route (the discovery document advertises
{issuer}/authorize) withresponse_type=code,client_id,redirect_uri,scope, and optionallycode_challenge+code_challenge_method=S256. - Your app authenticates the user, then calls
oidc.authorize({ ...params, userId })to issue a code. - Client exchanges the code at your token route (
{issuer}/token), which callsoidc.exchangeToken(...)and returnsaccess_token,id_token, andrefresh_token. - Client can refresh tokens using
grant_type=refresh_token. Refresh tokens rotate on each use.
PKCE with
S256 is supported. If the authorization request includes a code_challenge, the token request must include the matching code_verifier. Authorization codes are single-use and expire after 10 minutes by default.Endpoints
The module does not serve these routes. The discovery document returned bygetDiscoveryDocument() advertises the following URLs under issuer, and the table shows the module method each route should call:
Other module methods:
getClient, deleteClient, and validateAccessToken.
Related
OIDC provider logout
end_session_endpoint and back-channel logout.
OAuth overview
Using theAuth as an OAuth client to sign in via other providers.
SSO
Enterprise SSO via SAML 2.0 and OIDC connections.
MCP
OAuth 2.1 authorization server for MCP tool connections.
Authentication overview
All sign-in methods available in theAuth.