

Setup
There are two ways to use organizations, and thetheauth.org object used in the examples below only exists with the first one.
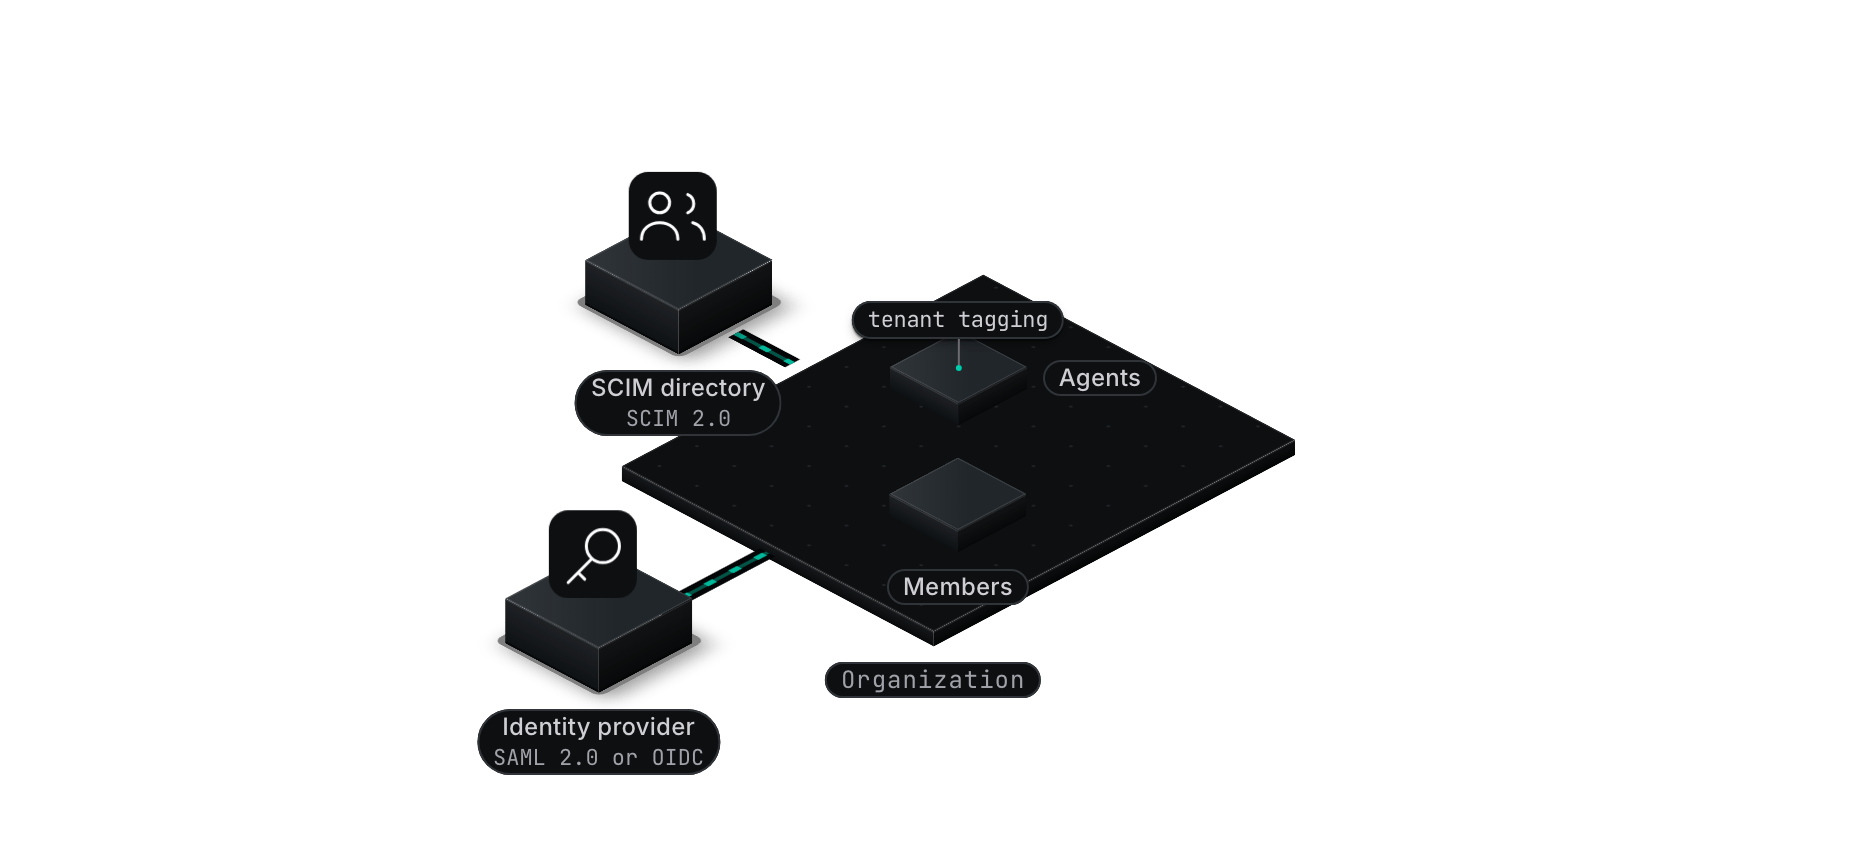
An identity provider and a SCIM directory feed an organization that holds members and agents.
theauth.org). Pass an org config object to createTheAuth. Without it, theauth.org is null and every theauth.org.* call below fails.
organization plugin). The organization() plugin registers /auth/org/* routes for an adapter to serve. It does not add theauth.org to the instance.
auth.adapter or an auth.session token.
The code samples below call theauth.org!.<method>(...). They assume the org config was passed. Use ?. instead of ! if you want to tolerate it being absent.
Creating organizations
owner role.
Inviting members
Managing members
Roles and permissions
Four built-in roles ship by default:
Check permissions at runtime:
Custom roles
Set
allowCustomRoles: false in the org config (or the plugin options) to restrict orgs to the built-in roles only.Configuration reference
Endpoints
organization() plugin
All plugin routes require an authenticated user.
theauth.org.handleRequest (module)
The module’s own handler serves a larger set of paths. It does no authentication, so only mount it behind your own checks.
Related
SSO
Enterprise SSO connections scoped to an organization.
SCIM
Automated user and group sync from your identity provider.
Admin
Cross-organization user management tools.
Permissions
Scoped permissions that integrate with org membership.